Execution Boundary
Where proposed model or agent behavior becomes consequential action, and whether that boundary can actually prevent inadmissible execution.
Defined System · Defined Boundary · Defined Evidence · Defined Determination
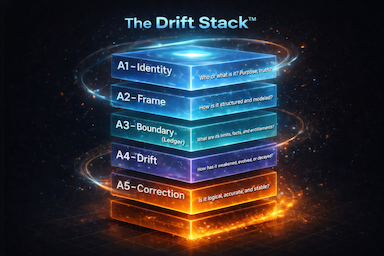
The Drift Stack™
Identity → Frame → Boundary → Drift → Correction
Technical examination
Conformance is not established because a system uses the right terminology, has an impressive architecture diagram, produces good model outputs, or maintains extensive logs.
The review examines whether a defined implementation actually enforces the mechanisms required to keep consequential execution admissible under current operational conditions.
Where proposed model or agent behavior becomes consequential action, and whether that boundary can actually prevent inadmissible execution.
Whether identity, delegated authority, scope, expiry, revocation, and current permission are validated before consequential execution.
Whether the system reconstructs and validates the state that exists now rather than relying on stale approvals, assumptions, memory, or earlier conditions.
Whether execution decisions are bound to attributable evidence, applicable policy, freshness requirements, constraints, and explicit reason codes.
Whether granted authority is narrowly constrained by action, target, time, value, tool, use, geography, data, and other applicable execution limits.
Whether realized effects are recorded and whether changed authoritative state can invalidate, suspend, reverse, compensate, or escalate execution.
The model may propose.
The system must prove that the proposed action remains admissible before consequence is allowed to bind.
The commercial path
Formal conformance cannot be responsibly priced before the system, boundary, maturity, evidence, and required testing are understood. That is why every engagement begins with the Architectural Review & Brief.
Step 1
Begin with the $500 private review of the actual system, architecture, proposal, implementation, or problem in front of you.
Step 2
Samirac determines whether formal conformance is appropriate and defines the exact application, execution boundary, evidence, domain profile, and review depth.
Step 3
If conformance is the correct next step, you receive a defined review scope, evidence requirements, testing expectations, commercial terms, and price.
Step 4
The implementation is examined against the agreed architecture, evidence, execution behavior, negative tests, and applicable conformance requirements.
The Architectural Review does not automatically lead to a Conformance Review.
It may determine that architectural remediation, implementation work, additional evidence, a different engagement, or no additional Samirac work should occur first.
Demonstration, not assertion
Evidence requirements depend on the approved scope. The formal technical standard defines the deeper requirement set; the items below illustrate the kind of implementation evidence a review may require.
Evidence must match reality
Policies, diagrams, prompts, dashboards, vendor claims, and architecture language may describe intended behavior.
The review is concerned with whether the implementation can actually demonstrate required behavior — including refusal, expiry, invalidation, constraint enforcement, receipts, and correction.
A defined result
A formal review is intended to produce a documented technical determination against the agreed system boundary and scope — not another general consulting conversation.
The deliverable may identify what was examined, what evidence was accepted, which mechanisms were demonstrated, where requirements were not satisfied, and what must occur before a stronger conformance or certification claim can be supported.
The examined implementation demonstrates the required mechanisms and evidence for the approved system boundary and review scope.
Material architectural or execution-control deficiencies must be corrected before the system can establish conformance.
The required mechanisms may exist, but available evidence is not sufficient to prove them, or the implementation is not yet mature enough for formal determination.
Where certification is included in the agreed scope and the system satisfies the applicable requirements, Samirac may authorize the corresponding reviewed-system certification claim under approved terms.
Any conformance or certification claim applies only to the examined system, defined boundary, approved version, and agreed scope.
It does not certify the entire company, every product, every deployment, or every future release.
Why there is no fixed public conformance price
A single agent, a contained internal application, a multi-agent orchestration platform, a financial execution system, and an enterprise deployment do not require the same examination.
Review effort changes with boundary size, implementation maturity, consequence level, number of integrations, evidence quality, domain requirements, execution pathways, negative testing, correction requirements, and certification scope.
That is why Samirac does not publish an artificial one-price conformance package.
The fixed-price entry point
$500
One private live review plus a concise written architectural determination of the primary issue and the right next step.
If formal conformance is appropriate, this review gives Samirac the basis to define and price it correctly.
Defined limits
Architecture · Scope · Evidence · Testing · Determination
Start by determining whether formal conformance is actually the right next step.
The $500 Architectural Review & Brief examines the real system or problem first. If formal conformance should follow, Samirac then defines the boundary, evidence requirements, review scope, tests, commercial terms, and price.
Formal Conformance Review is scoped and priced only after the system and review boundary are understood.